Complete components
Headers, plain text and HTML bodies, attachments, and metadata in a structured object.
Email analysis and security
SpamScope was created to analyze email: a channel used for phishing, fraud, credential theft, and malware delivery, often through social engineering.
Discover mail-parser EMAIL / STRUCTURE / EVIDENCE
The project
From the start, the decision was to extract mail-parser from the SpamScope platform and develop it as an independent library. Anyone can integrate it into their own tools to examine email messages, reconstruct their structure, and preserve evidence useful in forensic analysis.
Headers, plain text and HTML bodies, attachments, and metadata in a structured object.
Extract headers, bodies, attachments, and Received hops. Distinguish the display name from the mailbox in From while preserving the original value.
Detect address and MIME structure defects that may hide content or evasion techniques without discarding the raw evidence.
Access Python properties, raw values, and JSON in security and digital forensics workflows.
Analyze raw email messages and their MIME parts.
Convert Outlook files to .eml through an optional backend, then analyze their content.
From raw to structured
The animation uses a test message from the repository. The excerpt shows how an address-like display name can differ from the mailbox in From. It does not authenticate the sender’s identity.
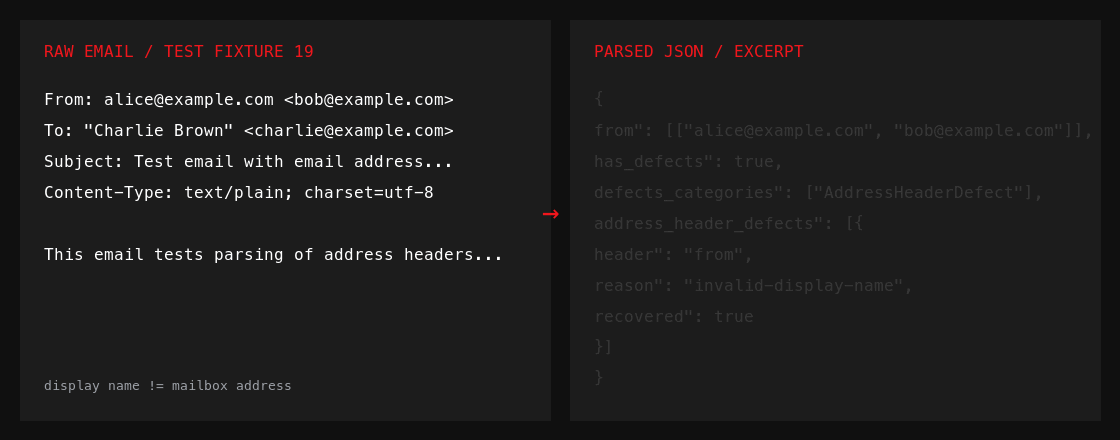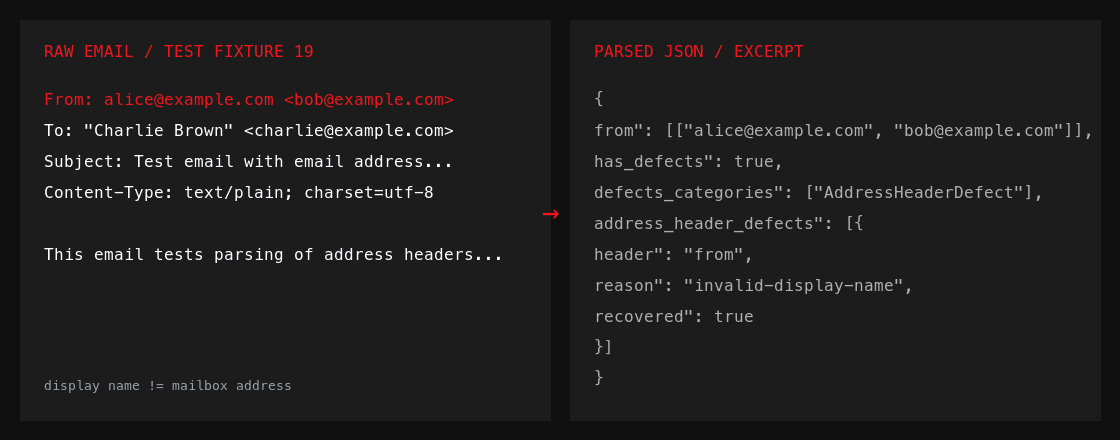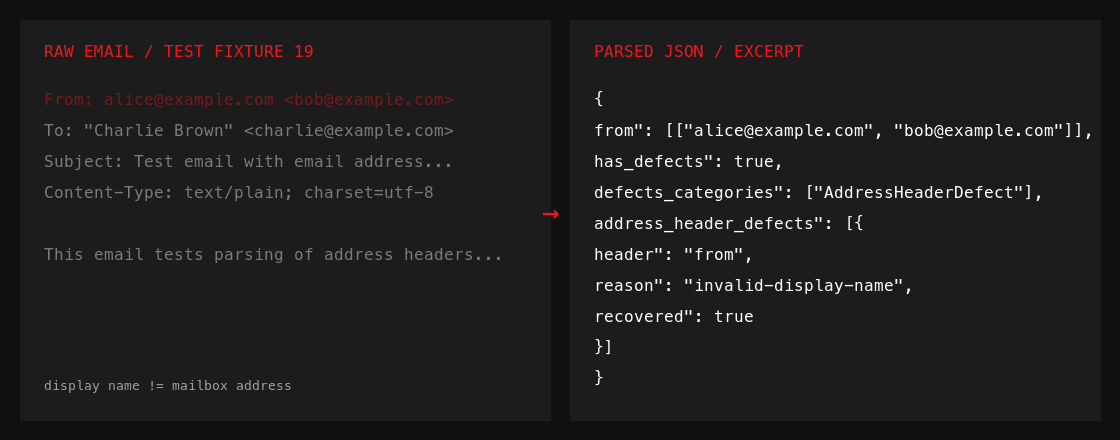
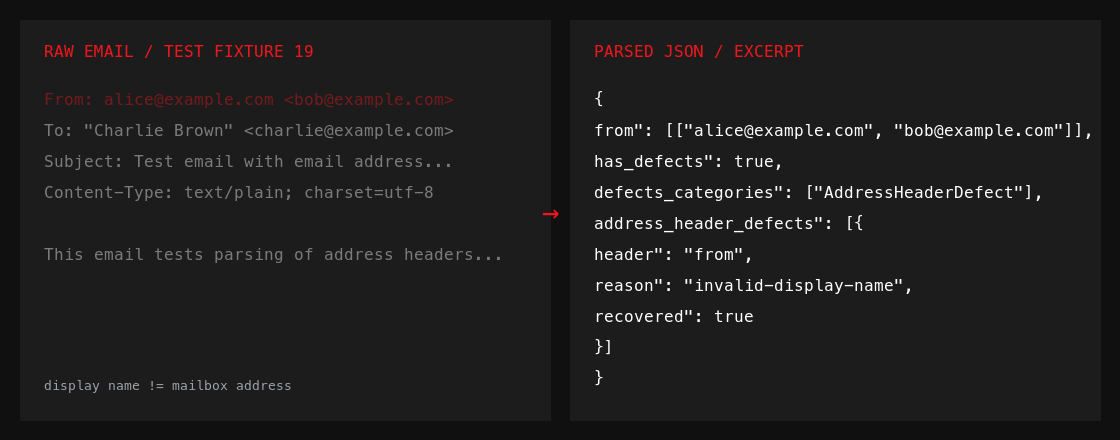
Abbreviated JSON output from the test fixture.
The ecosystem
The library appears in distributions and toolkits, is integrated into other tools, and is used in research.
 FreeBSDmail/py-mail-parser port ↗
 Arch Linuxmailparser AUR package ↗
 DebianSource package in sid ↗
 REMnuxMalware analysis toolkit ↗
Integrations
Parse Utilities uses mail-parser to extract headers, bodies, and attachments from .eml and .msg files in incident response workflows.
View the integration ↗Research
A study of 2.9 million phishing emails uses mail-parser to extract PDF, image, and calendar invitation attachments from their MIME structure.
Read the study ↗Adoption
mail-parser downloads from PyPI over the previous 30 days, checked on October 29, 2026. This counts downloads, not unique users.
Coming soon
MailXray is a self-hosted email threat-analysis platform. It brings together mail-parser and AI to help examine suspicious messages.
We’ll introduce it soon.